E-commerce and GDPR: What Online Businesses Need to Know
Updated: August 2026
For many online businesses, data protection has become a critical concern. With the introduction of the General Data Protection Regulation (GDPR) in 2018, organisations must follow strict guidelines to protect the privacy and security of personal data. This article explores the relationship between e-commerce and GDPR and what online businesses need to know.
Key Takeaways
• Online businesses that collect customer data, including names, addresses, payment details, and purchase history, need explicit, freely given consent for that collection, plus privacy policies and consent forms written in plain language rather than legal jargon.
• GDPR requires data minimisation (collecting only what’s needed for a specific purpose), 72-hour breach notification to supervisory authorities and affected individuals, and processes for handling data subject rights requests, including access, rectification, erasure, and data portability.
• Non-compliance risks fines of up to €20 million or 4% of global annual turnover, whichever is higher, on top of the reputational damage and lost customer trust that tends to follow a publicised breach or enforcement action.
GDPR – A Short Summary
The General Data Protection Regulation (GDPR) was introduced in 2018 by the European Union (EU) as a comprehensive data protection framework. Its primary objective is to protect the privacy and security of personal data belonging to individuals within the EU and the European Economic Area (EEA). GDPR applies to any organisation that collects and processes EU citizens’ personal data, regardless of its location.
The regulation defines personal data as any information that relates to an identified or identifiable natural person. This includes names, addresses, email addresses, financial information, and even IP addresses. GDPR gives individuals greater control over their personal data and imposes strict obligations on organisations to handle it responsibly.
Why should E-commerce brands be GDPR Compliant?
GDPR has significant implications for e-commerce businesses. Online retailers collect a lot of personal data, including customer names, addresses, payment details, and purchase history. These businesses must understand how GDPR affects their operations and take the steps needed to ensure compliance.
Consent and Transparency
Under GDPR, organisations must obtain explicit and freely given consent from individuals before collecting and processing their personal data. This means e-commerce businesses must be transparent about how they use customer data and give individuals the option to opt in or opt out of data collection. Consent forms and privacy policies should be clear, concise, and written in plain language.
Data Minimisation and Purpose Limitation
Another fundamental GDPR principle is data minimisation. E-commerce businesses should collect and retain only the minimum personal data needed to fulfil the intended purpose. Moreover, organisations must specify the purpose for which they collect data and ensure they do not use it for other purposes without obtaining additional consent.
Data Security and Breach Notification
Data security is critical in e-commerce. GDPR requires organisations to implement appropriate technical and organisational measures to protect personal data from unauthorised access, loss, or disclosure. In the event of a data breach, businesses must notify the relevant supervisory authorities and affected individuals within 72 hours of becoming aware of the breach.
Individual Rights
GDPR grants individuals several rights regarding their personal data. E-commerce businesses must be prepared to address these rights, which include the right to access, rectify, and erase personal data and the right to data portability. Organisations should have processes in place to handle data subject requests and give individuals the information and tools they need to exercise their rights.
Best GDPR practices for e-commerce businesses
Complying with GDPR can be a complex undertaking for e-commerce businesses. However, by following a few key steps, online retailers can ensure they meet their obligations and protect customer data.
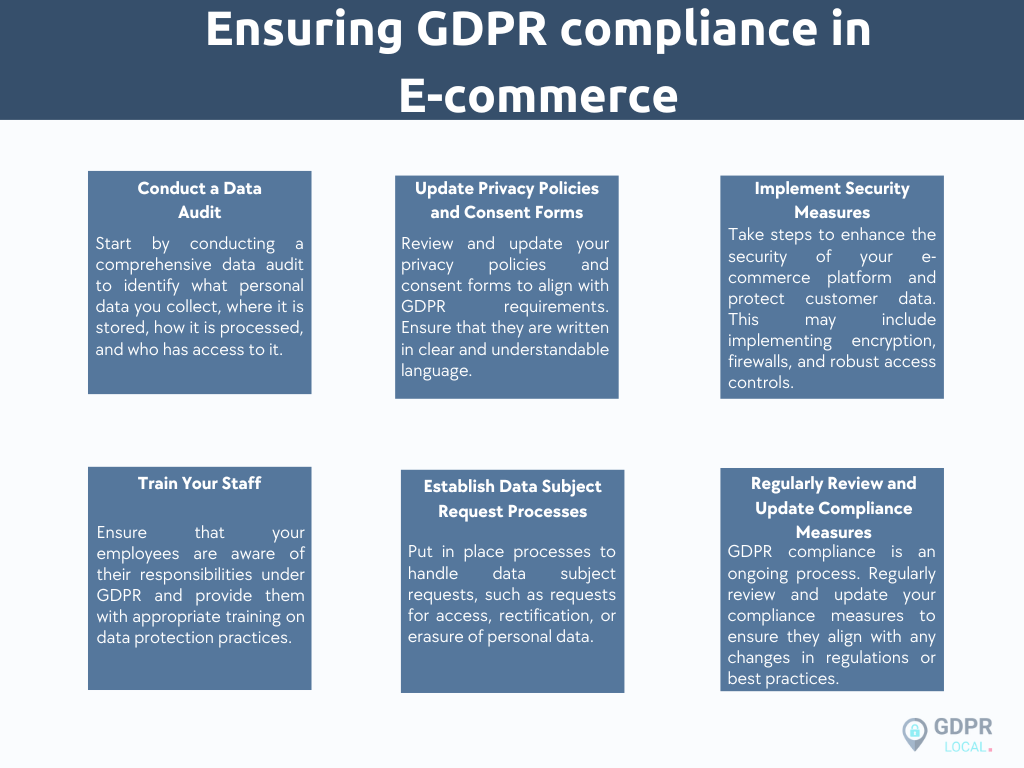
You can audit your data processing activities to identify compliance gaps or potential risks. By updating the privacy and consent forms, people will know how their data is processed and what rights they have under GDPR.
By monitoring your systems for vulnerabilities or suspicious activity, you can promptly address issues as they arise.
Training your staff will help your employees understand the importance of safeguarding personal data and ensure compliance throughout your organisation.
Designate a point of contact within your organisation to handle these requests and establish clear procedures for verifying the identity of data subjects.
Additionally, stay informed about new developments in data protection and adjust your practices accordingly.
What are the penalties if your e-commerce brand is not GDPR compliant?
Non-compliance with GDPR can lead to serious financial and reputational consequences for e-commerce businesses. Supervisory authorities can impose fines of up to €20 million or 4% of your company’s global annual turnover, whichever is greater, depending on the severity of the violation. These penalties apply to various infringements, including improper data handling, lack of user consent, and failure to respond to data subject requests. Beyond fines, your business may face investigations, legal challenges, and a significant loss of customer trust, which can severely impact your brand’s credibility and bottom line.
Common Mistakes E-commerce Businesses Make Regarding GDPR
Many e-commerce businesses struggle with GDPR compliance due to common oversights. One frequent mistake is using pre-ticked consent boxes or vague privacy policies that don’t clearly explain how customer data is used. Others collect more data than necessary or retain it longer than required, violating the principles of data minimisation and purpose limitation. Inadequate security measures or delayed responses to data breaches can lead to non-compliance. Additionally, some businesses neglect to provide clear procedures for handling data subject rights, such as access or deletion requests. Avoiding these mistakes starts with adequately understanding GDPR and building privacy into every level of your data processing operations.
How can GDPRLocal help?
Navigating GDPR compliance can be challenging for e-commerce businesses. We offer comprehensive solutions to help online retailers achieve and maintain GDPR compliance.
GDPR Audit and Compliance Assessment
We can provide a thorough audit and compliance assessment to identify non-compliance areas and recommend remedial actions. Our team of experts examines your data processing activities, privacy policies, consent forms, and security measures to ensure they align with GDPR requirements.
Data Protection Officer (DPO) Services
A dedicated Data Protection Officer (DPO) service helps e-commerce businesses meet GDPR obligations and strengthen their data protection. Our responsibilities include providing guidance, monitoring compliance, and acting as a liaison between your organisation and supervisory authorities.
Data Subject Request Management
Handling data subject requests can be time-consuming and complex. We streamline this process by managing them on your behalf. We handle requests for access, rectification, erasure, and data portability, ensuring compliance and timely responses.
Ongoing Compliance Support
If you need ongoing data protection support, we are here to help with any compliance-related issues.
Conclusion
As e-commerce continues to thrive, data protection shouldn’t be overlooked. GDPR has significantly changed how online businesses handle personal data, requiring organisations to prioritise transparency, security, and individual rights. By understanding GDPR’s implications and implementing the necessary measures, e-commerce businesses can ensure compliance and build trust with customers.
For more information on how GDPRlocal can help your e-commerce business achieve GDPR compliance, contact us.
Frequently Asked Questions
Does GDPR apply to e-commerce businesses outside the EU?
Yes. GDPR applies to any business that collects or processes the personal data of people in the EU, regardless of where the business itself is located. An online store based outside the EU still needs to comply if it sells to or tracks customers in the EU.
What personal data does GDPR cover for an online store?
Any information that relates to an identified or identifiable person, which for e-commerce typically includes names, addresses, email addresses, payment details, purchase history, and IP addresses.
How quickly must an e-commerce business report a data breach?
Within 72 hours of becoming aware of it, businesses need to notify the relevant supervisory authority and, where the breach poses a risk to people’s rights and freedoms, the affected individuals too.
What are the most common GDPR mistakes e-commerce businesses make?
Pre-ticked consent boxes, vague privacy policies, collecting more data than needed or keeping it longer than necessary, weak security measures, slow breach responses, and no clear process for handling data subject requests like access or deletion.
About the Author
Head of Commercial & Country Manager
Zlatko Delev is Head of Commercial and Country Manager at GDPRLocal, where he leads the company’s commercial strategy and market presence. He brings international experience across sales, marketing, and customer success, along with a legal background from his studies at Iustinianus Primus Law School in Skopje, Macedonia.
Zlatko sits at the front line of GDPRLocal’s client relationships, guiding organisations through the first stages of their compliance journey and helping them understand where they stand and where they need to go on GDPR, information security, and the emerging landscape of AI regulation. His role bridges commercial strategy with practical data protection knowledge, ensuring clients get clear, actionable direction from their very first conversation with GDPRLocal.
Alongside his commercial focus, Zlatko has trained extensively in project management and organisational leadership, including risk management, stakeholder communication, agile methodology, and digital marketing, a broad skill set that supports his structured, delivery-focused approach to growing GDPRLocal’s business internationally.